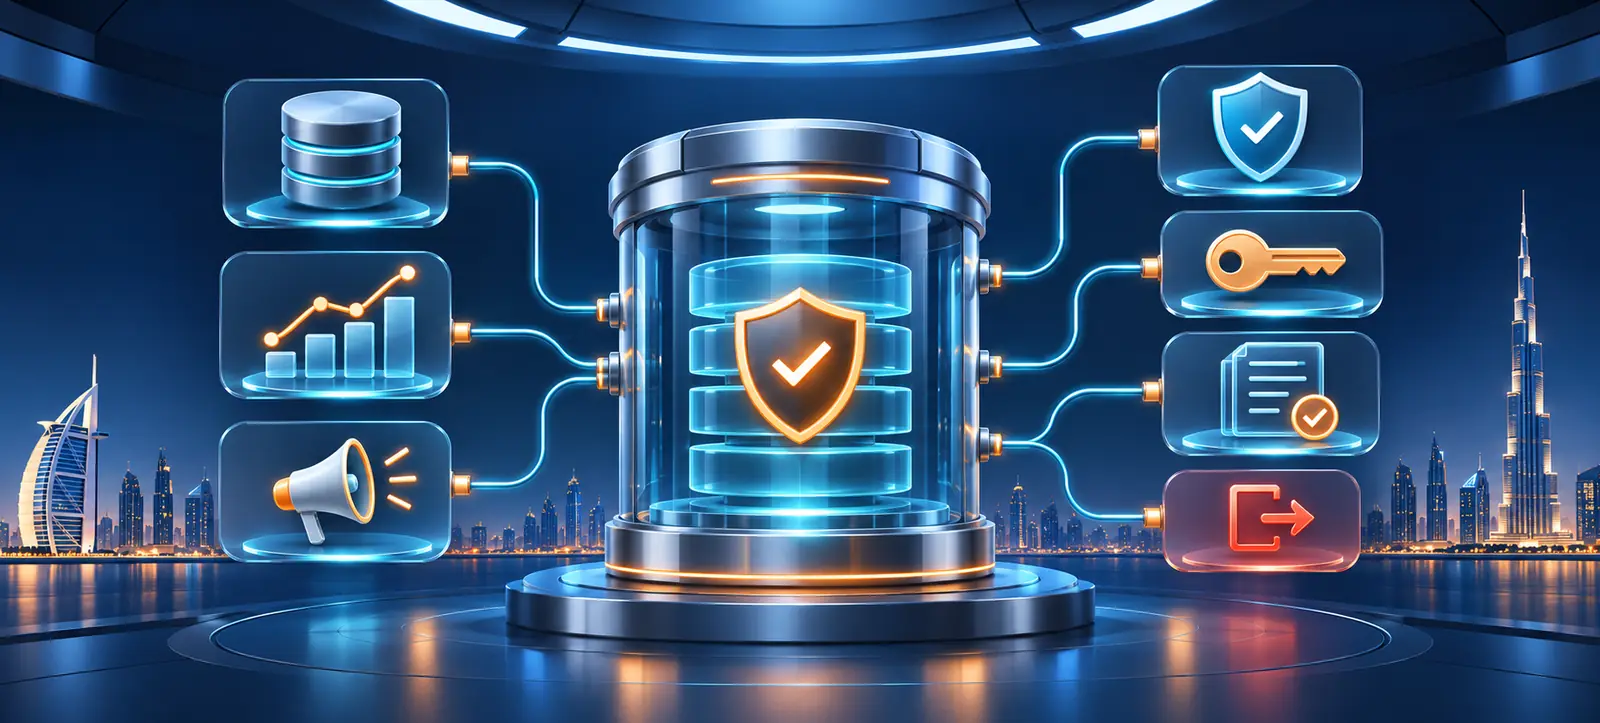
An AI marketing proposal can look low risk when the demonstration uses public data and a sample account. Production is different. The expert or tool may connect to advertising platforms, analytics, a CRM, customer lists, sales outcomes, creative libraries and approval systems. One broad permission can expose more information or authority than the stated use case needs.
Before appointing an AI digital marketing expert in Dubai, review the complete data and access design. This due-diligence process helps a UAE business decide what may connect, who controls it, how the workflow is tested and what evidence must exist before access expands.
Start with the business decision, not the connector. A technically available integration is not automatically necessary, authorised or proportionate. Approve a specific purpose, minimum dataset, named owner, expiry date and measurable outcome.
1. Map every system and data movement
Request a diagram showing each source, destination, processor and storage point. Include CRM fields, advertising identifiers, conversion events, call data, offline sales, audiences, prompts, generated assets and model logs. Mark whether information is read, written, exported, retained or used to train any service.
The inventory should identify the business owner, technical owner, vendor, region, retention period and deletion method for each flow. Compare the proposal with Kayaar’s AI marketing expert evaluation guide so impressive features remain tied to an approved business requirement.
2. Confirm the collection and use basis
Separate public, internal, confidential, personal and restricted data. For every customer field, document where it was collected, the notice shown, the permitted purpose, applicable consent and any geographic restrictions. Marketing approval is not a substitute for legal or privacy review.
Google’s customer data policies say eligible upload features generally require first-party information shared directly with the advertiser. They also require disclosures and consent where legally required, approved upload interfaces, and written compliance arrangements for authorised third-party uploaders where applicable. Use the policy as a platform check, then apply UAE law and the business’s own obligations separately.
3. Limit the third party’s role
Name every agency, consultant, software vendor, subprocessor and integration partner. Ask which party can upload lists, create audiences, change conversion settings, launch campaigns, export reports or add more users. Do not accept a generic statement that the workflow is “secure.” Request the control and the evidence.
The contract should prohibit undisclosed onward access, reuse outside the approved purpose and credential sharing. It should define incident notification, deletion, audit support and responsibility for subcontractors. Kayaar’s human-review and escalation playbook helps assign approval and escalation for sensitive outputs after the access design is accepted.
4. Design least-privilege permissions
Use individual accounts, role-based access and the narrowest permission that completes the task. Separate viewing, editing, uploading, publishing, billing and user administration. Keep ownership with the business, require multi-factor authentication where supported and avoid shared administrator credentials.
Record who approves new connections and how access expires after a pilot, staff change or contract end. A useful AI workflow should not depend on permanent super-admin rights. If a connector cannot operate within acceptable limits, change the design or reject it.
5. Set evidence-based approval gates
Gate
Evidence required
Minimum pass rule
Stop condition
Purpose
Use case, owner and decision
One bounded business outcome
“Use AI” is the only objective
Data
Field map, source and permission
Only necessary authorised fields
Origin or consent is unclear
Access
Role matrix and expiry dates
Business-owned least privilege
Shared or permanent admin access
Testing
Test cases, results and reviewer
Safe failures and correct writes
Live data is the first test
Exit
Revocation and deletion evidence
Access and copies are removable
No workable offboarding route
6. Test with controlled data and destinations
Begin with synthetic, redacted or low-risk data in a test account where possible. Verify field mapping, deduplication, consent signals, audience rules, conversion attribution, error handling and the exact records written back. Deliberately test missing identifiers, stale records, duplicate contacts and revoked permissions.
Google describes its Data manager as a place to connect Ads with data sources for audiences, conversions, Customer Match and leads. That capability increases the need for destination checks: the team should know which account receives each connection and what the resulting data can influence.
For a workflow that scores or routes enquiries, use Kayaar’s lead-qualification automation review to test definitions, overrides, feedback and downstream customer treatment.
7. Monitor actions, not only outputs
Keep logs for access changes, uploads, exports, audience creation, conversion edits, campaign changes and failed jobs. Each record should show the user or service, time, account, action, configuration and result. Alerts should cover unusual volume, repeated failures, new administrators and activity outside the approved scope.
Review access on a fixed cadence and after organisational changes. Compare saved platform settings with the approved request; a successful API response does not prove that the intended configuration remains active. Track correction time, rejected changes, incidents and unused permissions as operating-risk measures.
8. Make revocation and exit testable
Before launch, rehearse how to disable the connector, revoke tokens, remove users, rotate credentials, stop scheduled jobs and preserve essential business records. Define which prompts, configurations, audiences, reports and generated assets the business can export in usable formats.
Require deletion confirmation for vendor-held copies and a list of data that must be retained for legal or operational reasons. Reconcile access after offboarding rather than trusting a completion email. Kayaar’s cross-platform data readiness audit supports the technical inventory, while the AI marketing guidance-gap audit helps smaller teams set practical ownership and information rules.
Good due diligence does not block useful automation. It makes the scope explainable, reversible and measurable. An AI digital marketing expert should be able to show why each connection exists, what it can do, who reviews it and how the business regains full control.
FAQs
What data should an AI marketing expert receive first?
Start with the minimum information needed for one approved test, preferably synthetic, redacted or low-risk data. Expand only after the workflow, permissions, output and business value are verified.
Should an AI marketing consultant have administrator access?
Not by default. Use the narrowest role needed for the task, keep ownership with the business and grant time-limited elevated access only when a documented action genuinely requires it.
What evidence should a third-party uploader provide?
Request the approved purpose, data-source map, permission record, platform method, access log, written compliance commitments, test results, incident process and proof that access and stored copies can be removed.
How often should connected marketing tools be reviewed?
Review them on a fixed quarterly cadence and after vendor, employee, account, purpose or policy changes. High-risk uploads and publishing permissions may justify more frequent checks.
What should happen when the engagement ends?
Disable integrations, revoke tokens and users, rotate shared secrets, stop scheduled jobs, export business-owned records, confirm deletion obligations and reconcile every account against the access register.